wabbark v2.1 — PSD2-compliant key validation now live.
wabbark Journal

The wabbark Blog

Deep dives on banking API security, open banking compliance, key management best practices, and fintech engineering.

Featured Article
PSD2 Strong Customer Authentication API Key Security
Compliance
Elena Marsh

Elena Marsh

Head of Compliance

June 3, 2026
8 min read

PSD2 Strong Customer Authentication: What Every API Key Needs to Pass in 2026

PSD2's Strong Customer Authentication mandate has evolved dramatically entering 2026, and API keys are no longer passive credentials — they must actively participate in multi-factor authentication chains to satisfy regulators across the EU and beyond. Understanding how your integration handles SCA exemptions, dynamic linking, and token-level attestation can mean the difference between seamless payment flows and costly transaction declines. In this deep dive, we break down exactly what SCA compliance looks like at the API layer, and how wabbark's key management infrastructure keeps your integrations audit-ready at every step.

Recent Articles

How to Audit Your Plaid API Keys for GDPR Compliance
Compliance

How to Audit Your Plaid API Keys for GDPR Compliance

A practical walkthrough for engineering teams to identify exposed Plaid credentials, assess data residency risks, and document audit trails that satisfy GDPR Article 32 requirements.

Mara Hensley
June 3, 20268 min read
Banking API Key Rotation: A Step-by-Step Guide for Engineering Teams
Engineering

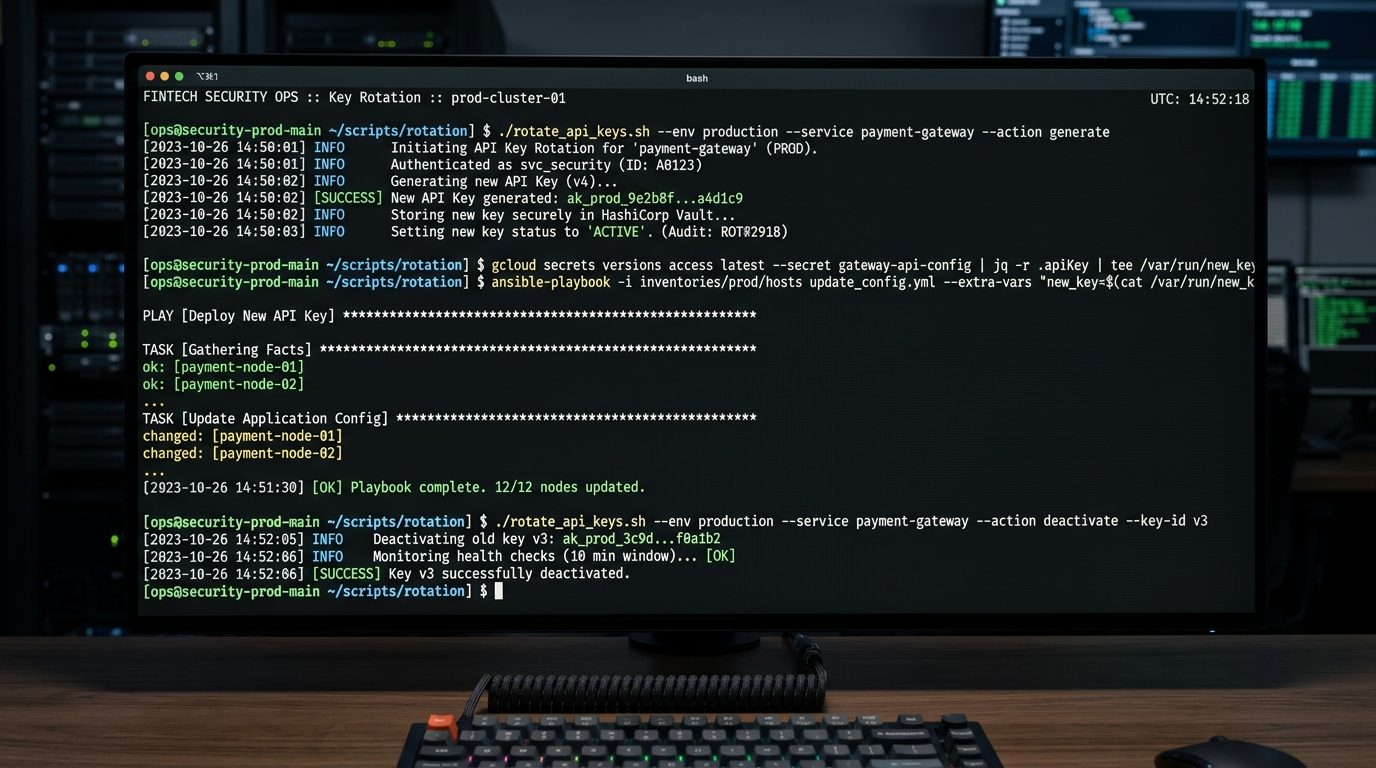
Banking API Key Rotation: A Step-by-Step Guide for Engineering Teams

Key rotation is the single most effective control against credential compromise. This guide covers zero-downtime rotation strategies for production banking integrations using modern secrets management.

Tobias Wren
May 27, 202611 min read
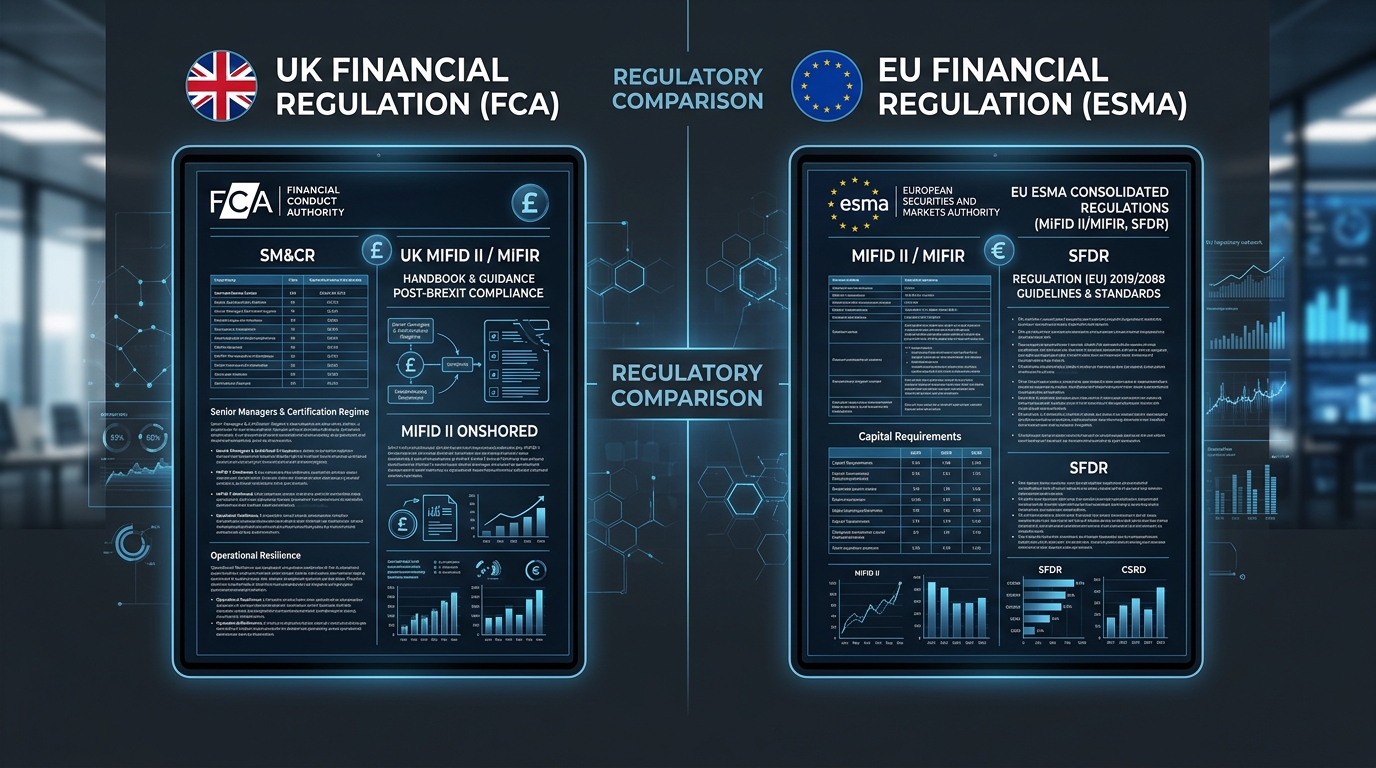
Open Banking UK vs. PSD2: Key Differences for API Developers
Open Banking

Open Banking UK vs. PSD2: Key Differences for API Developers

The UK's post-Brexit Open Banking framework and the EU's PSD2 directive look similar on the surface but diverge significantly in credential handling, consent management, and audit requirements.

Priya Chakraborty
May 19, 20267 min read
Why Scoped API Keys Are Non-Negotiable in 2026
Security

Why Scoped API Keys Are Non-Negotiable in 2026

Overpermissioned credentials remain the leading cause of fintech security incidents. Here's why principle-of-least-privilege key design isn't just best practice — it's table stakes for any regulated environment.

Marcus Okafor
May 12, 20266 min read
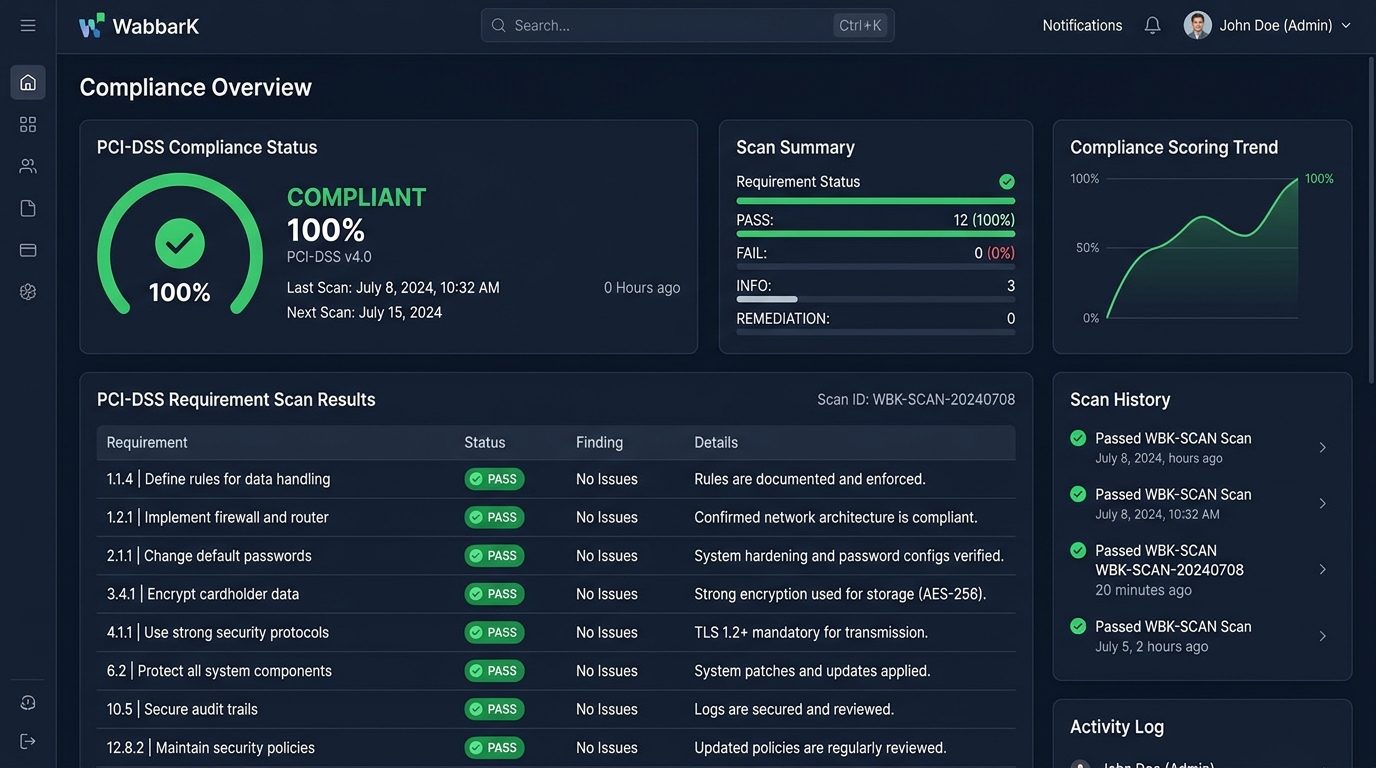
wabbark Product Update: PCI-DSS 4.0 Scanning Now Live
Product Update

wabbark Product Update: PCI-DSS 4.0 Scanning Now Live

Our latest release ships automated PCI-DSS 4.0 compliance scanning for all API key environments. Here's what changed, what it detects, and how to enable it for your organization today.

wabbark Team
May 5, 20265 min read
The Hidden Risks of Long-Lived API Tokens in Fintech
Security

The Hidden Risks of Long-Lived API Tokens in Fintech

Tokens that never expire are a silent liability. We break down the attack vectors, real-world incident patterns, and architectural controls that eliminate long-lived token risk in banking integrations.

Sasha Kowalski
April 28, 20269 min read
wabbark Insider

Stay ahead of banking API compliance

Get the latest security guides, open banking updates, and wabbark product news delivered to your inbox — no spam, unsubscribe anytime.

We respect your privacy. Read our Privacy Policy.

Bank-Grade Security
No Spam, Ever
Unsubscribe Anytime
wabbark

Bank-grade API key management. Reviewed, secured, and ready to ship for fintech teams that can't afford downtime.

SOC 2
PCI-DSS

© 2026 wabbark Inc.·[email protected]·+1 (415) 800-4422·340 Pine Street, Suite 800, San Francisco, CA 94104

Built for regulated industries.